 yoga-mahendra
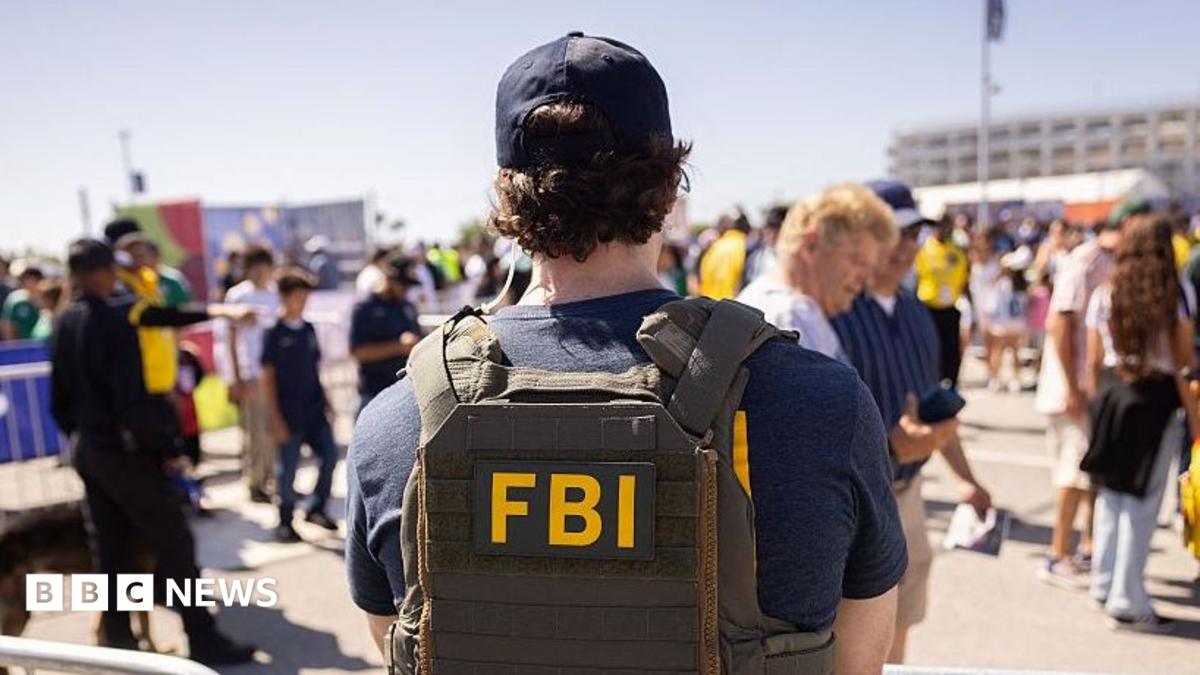
Dutch law enforcement officials have taken a 24-year-old man from Amsterdam into custody on suspicion of belonging to ShinyHunters, the cyber-crime collective that recently claimed responsibility for stealing sensitive data belonging to tens of thousands of FBI employees. The arrest, announced by Dutch police, marks a significant development in an international investigation into one of the more brazen hacking outfits currently operating.
According to authorities, the suspect was apprehended on 15 September, several days before the supposed FBI intrusion took place. Police have not disclosed what initially drew their attention to the man, but they confirmed that his electronic devices were seized and examined. A forensic review of his laptop allegedly uncovered a substantial trove of information, including material related to two planned killings abroad that investigators believe he may have commissioned.
The arrest carries a dual significance. Not only do Dutch officials suspect the man of participating in ShinyHunters' wider campaign of digital extortion and data theft, but they also accuse him of attempted incitement to commit two murders. The intersection of cyber-crime and violent criminal plotting underscores the evolving threat posed by ransomware and hacking groups, which increasingly operate with the resources and ruthlessness of traditional organized crime syndicates.
ShinyHunters itself has built a reputation for carrying out high-profile intrusions against major corporations and institutions. The group is thought to have originated in France and operates as an international collective, with members scattered across multiple jurisdictions. Its past victims include Rockstar Games, which was breached in April, and the education technology platform Canvas, which suffered a disruptive attack in May that affected students and educators across the United States.
The alleged FBI breach, which ShinyHunters claims to have executed on 21 September, targeted a cloud storage system that the bureau relies upon. According to the group's own account, hackers exploited a vulnerability in Oracle's cloud infrastructure to access multiple FBI systems. Among the compromised platforms were FBIJOBS, which handles recruitment; FBI BEAST, which processes background checks for employees and applicants; FBI MedLink, which stores agents' medical records; and FBI BICS, which contains investigative information.
The scope of the purported leak is enormous. ShinyHunters asserts it obtained the names, roles, badge numbers, home addresses, and telephone numbers of approximately 38,000 FBI personnel. The BBC has reviewed a small sample of the data and found it to appear authentic, though the full extent of the breach has not been independently verified.
What makes the incident particularly unusual is the group's stated motive. In a message posted on the dark web, ShinyHunters insisted it did not hack the FBI for financial gain. Instead, the cyber-criminals demanded that the bureau retract a public service announcement issued in May that characterized the gang as "threat actors" who exaggerate their access to sensitive information in order to extract payments from victims. The advisory, which remains on the FBI's website, also accuses the group of targeting major companies across the technology, finance, and retail sectors, often stealing millions of customer records in a single operation.
ShinyHunters claimed to have been "offended" by the FBI's description of its methods and motivations. The demand for a retraction is a striking departure from the typical demands of ransomware gangs, who usually seek cryptocurrency payments. It suggests the group is at least partly driven by a desire for notoriety and reputational legitimacy within the murky ecosystem of underground hacking forums.
The Dutch arrest has prompted reactions from senior FBI officials. Bureau director Kash Patel expressed gratitude to Dutch partners in a post on X, stating that FBI teams were actively working to pursue additional leads generated by the arrest. Brett Leatherman, assistant director of the FBI's Cyber Division, issued a pointed message to ShinyHunters members still at large, urging them to surrender while they still had the opportunity.
Leatherman warned that other criminal groups had mistakenly believed anonymity or loyalty among associates would shield them from prosecution, only to discover that arrests often loosen tongues and fracture trust. He added that the longer individuals remain involved in such operations, the more investigators learn about them, and that the FBI knows how to locate those it seeks.
Stan Duijf, who heads Dutch investigations into cyber-crime, described ShinyHunters as responsible for a large number of victims both domestically and internationally. He welcomed the arrest as a positive step in the ongoing effort to dismantle the group's operations. Dutch authorities have not ruled out the possibility of further detentions as the investigation continues.
The case raises broader questions about the vulnerability of government cloud infrastructure and the challenges of protecting sensitive personal data from determined attackers. The fact that ShinyHunters allegedly gained access to medical records and background check files—information of immense value to foreign intelligence services and criminal organizations alike—highlights the stakes involved. For the thousands of FBI employees whose personal details may now be circulating on the dark web, the breach represents not only a professional embarrassment for the bureau but a personal security risk that could persist for years.
The arrest of a suspect in Amsterdam also illustrates the increasingly global nature of cyber-crime investigations. Successful prosecutions often depend on rapid cooperation between law enforcement agencies in multiple countries, each bringing different legal tools and resources to bear. While the Dutch action is a notable victory, it remains unclear whether it will meaningfully disrupt ShinyHunters' operations or merely prompt the group to adapt and regroup.
For now, the man from Amsterdam remains in custody. His devices are being scrutinized, and the information recovered from his laptop—particularly the details concerning the alleged murder plots—could lead to charges far more serious than cyber-crime alone. As the investigation widens, authorities in the Netherlands and the United States appear determined to send a message that even those who hide behind encrypted channels and anonymized identities are not beyond reach.






Comments (0)